reaper@re4perz3d:~/certs$ cat ecir.md
eCIR — Certified Incident Responder
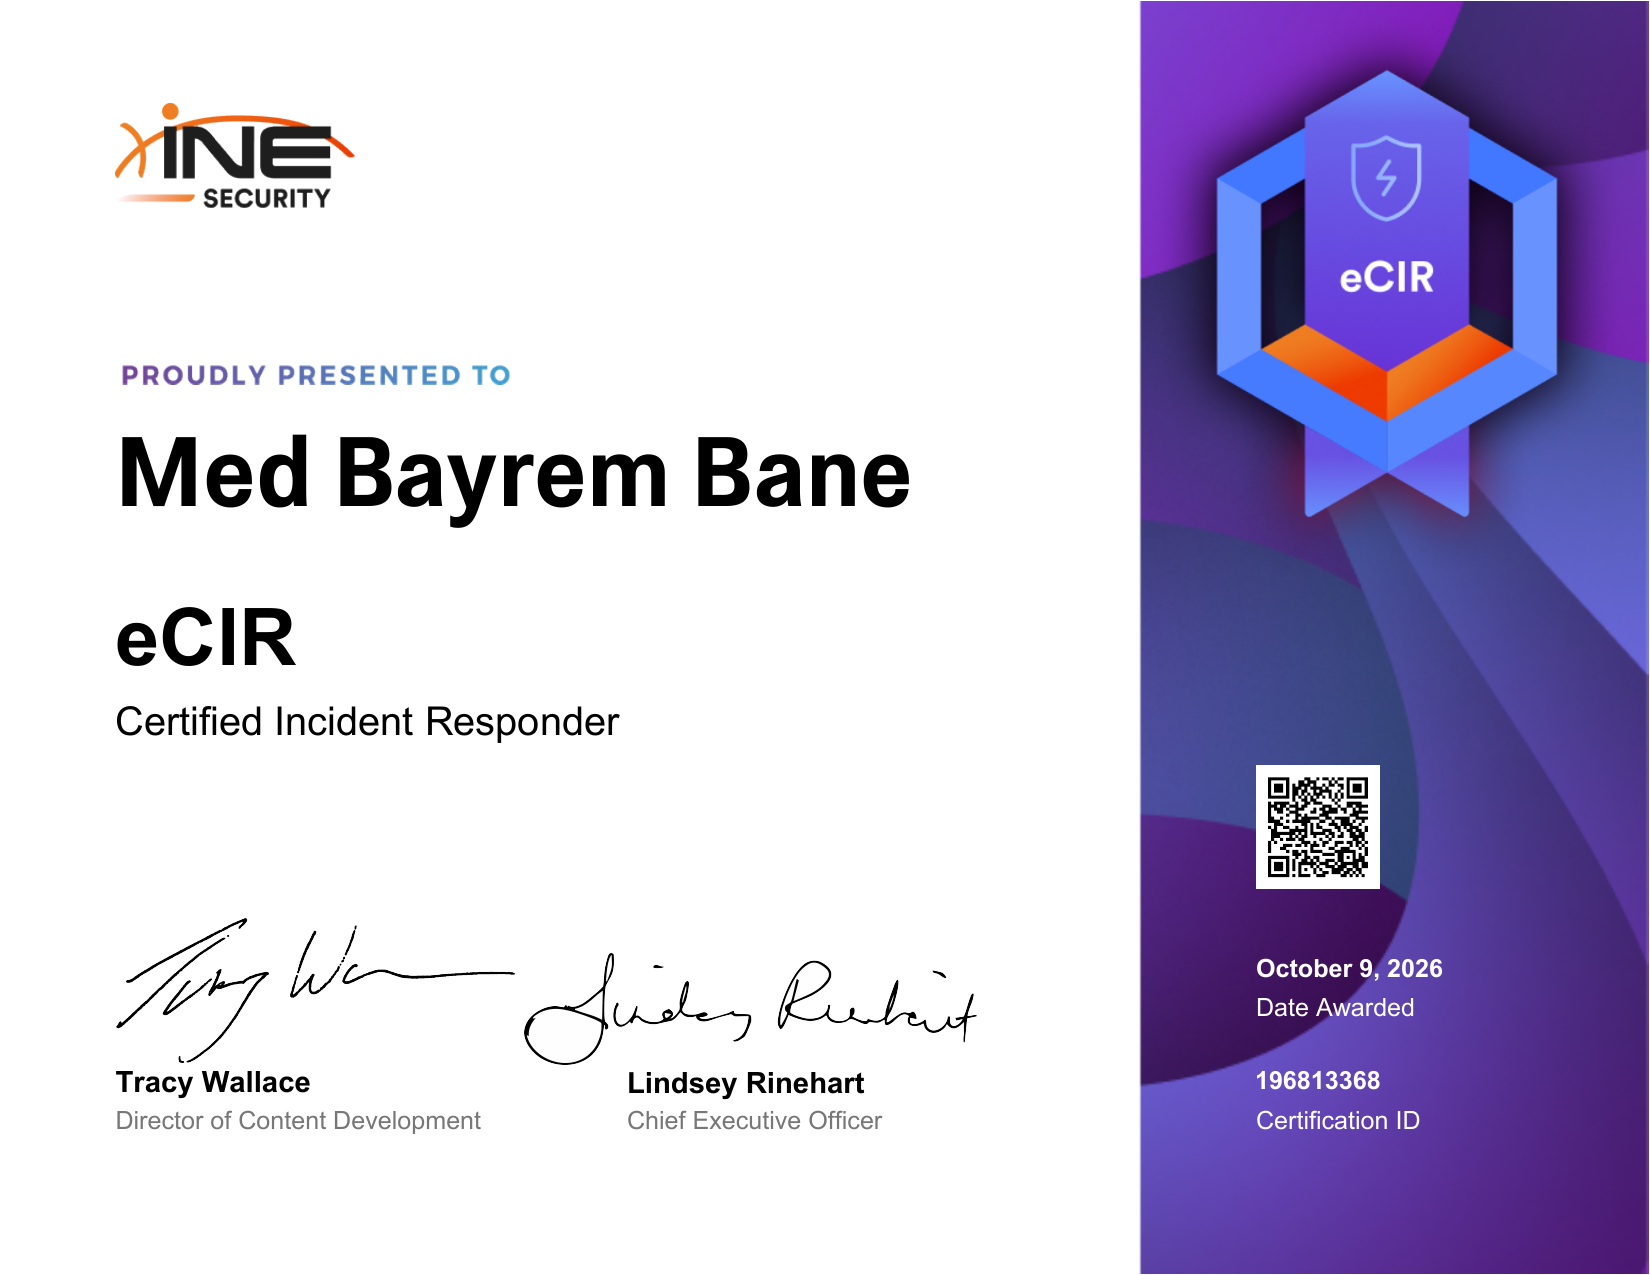
eCIR is INE’s practical incident-response certification. Instead of multiple-choice theory, you’re handed a compromised environment and have to work it the way a real IR engagement goes: detect, scope, contain, and explain what happened.
What I learned
- Triage under time pressure: deciding what to look at first when you don’t yet know what the incident is.
- Host-based forensics: pulling evidence from memory, the filesystem and the registry to reconstruct attacker activity on Windows and Linux hosts.
- Network traffic analysis: tying host artifacts back to PCAP evidence to confirm C2 and lateral movement.
- Log analysis and timeline building: correlating scattered events into a single, defensible incident timeline.
- Writing it up: turning a technical investigation into a clear incident report a non-technical stakeholder can act on.
Why it matters to my work
This is the closest a certification gets to my actual day job. I triage and close alerts in a SOC every shift, and eCIR is the same muscle: take ambiguous evidence, figure out what really happened, and be able to defend the conclusion. It also sharpened the forensics side of writeups like my Operation GhostVein piece.
$ verify --credential
Verify credential →