reaper@re4perz3d:~/certs$ cat ecpptv3.md
eCPPTv3 — Certified Professional Penetration Tester
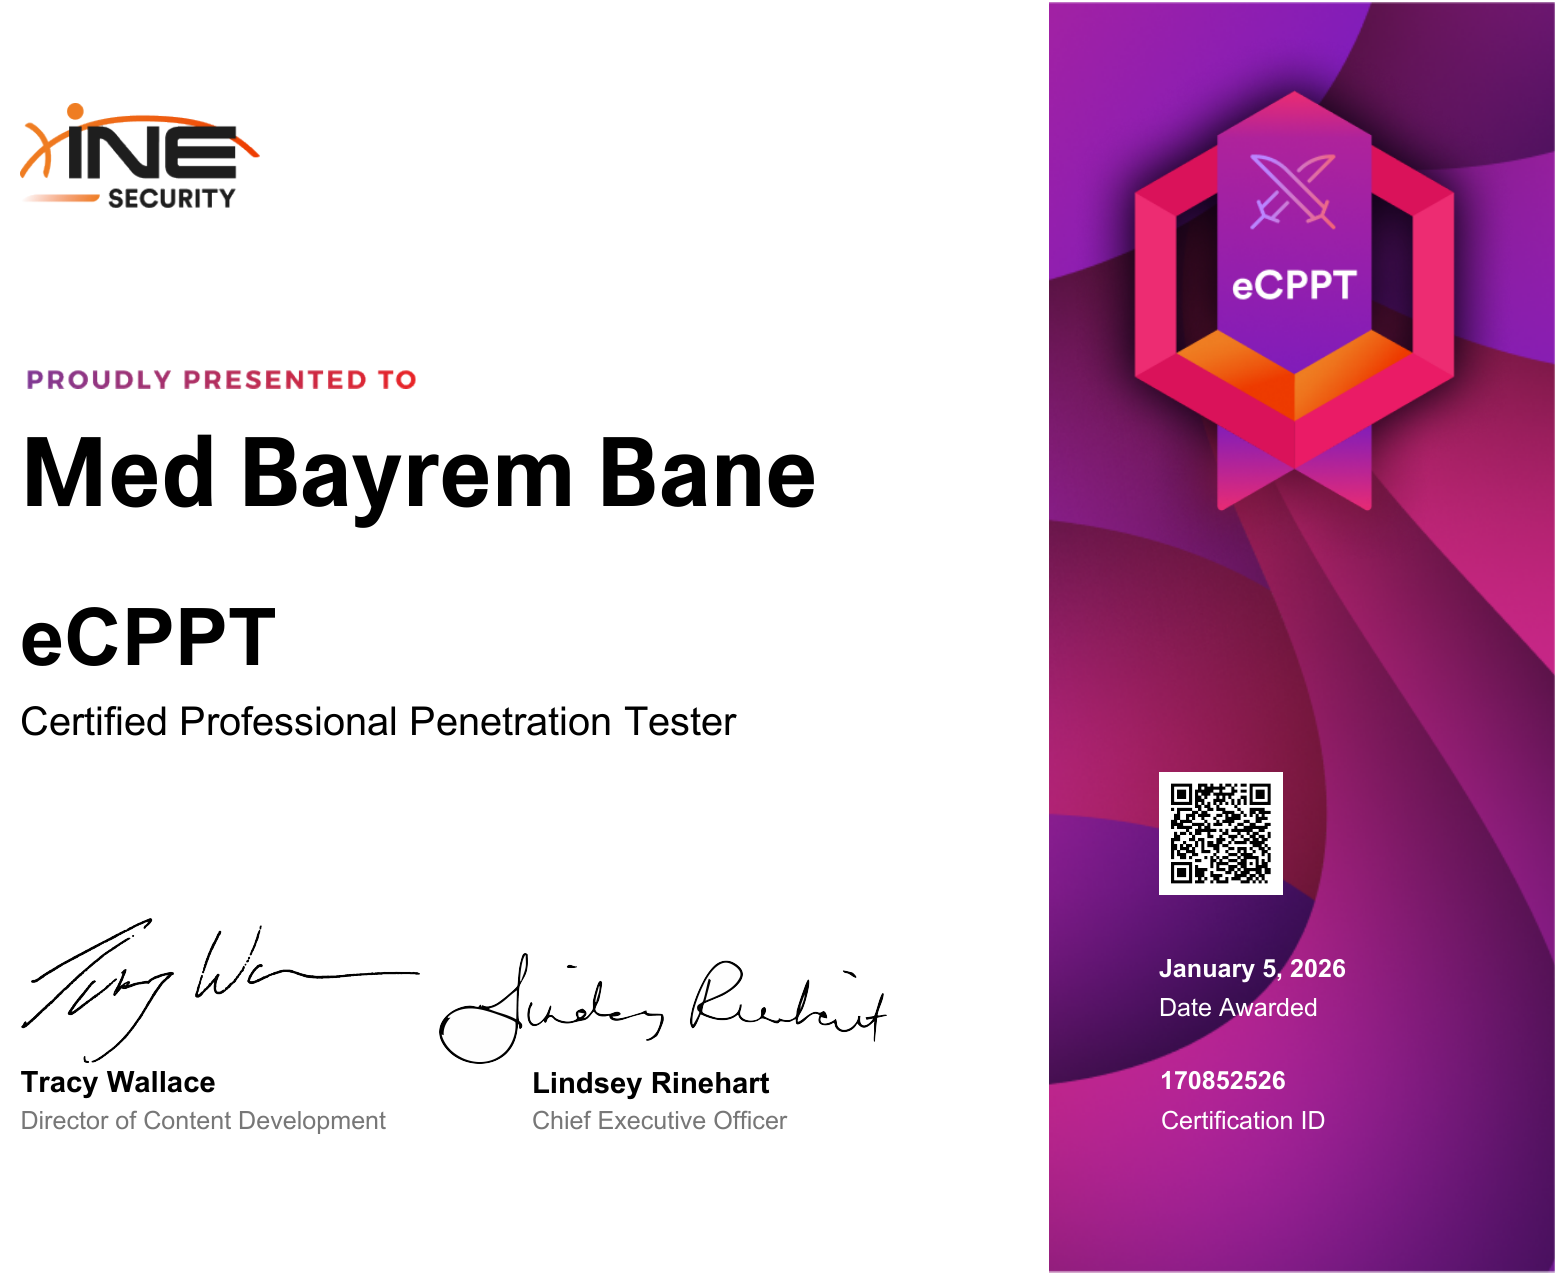
eCPPTv3 is INE’s practical penetration-testing certification. It tests the full chain, from enumeration to a foothold to a fully compromised network, on real machines.
What I learned
- A repeatable methodology: scoping, enumeration, exploitation, post-exploitation, and documenting what I did.
- Exploiting hosts and services with Nmap, Metasploit and manual techniques when the automated route fails.
- Privilege escalation on Windows and Linux. Windows privilege escalation was the hardest part for me and taught me the most.
- Pivoting through compromised hosts to reach internal networks that are not directly visible.
- Active Directory fundamentals on the offensive side, which later made CRTP much easier to approach.
Why it matters to my work
It trained me to think in attack chains instead of single findings. When I investigate an alert in the SOC, I now ask what the attacker would try next and where that step would appear in the logs.
$ verify --credential
Verify credential →