reaper@re4perz3d:~/certs$ cat ecthp.md
eCTHP — Certified Threat Hunting Professional
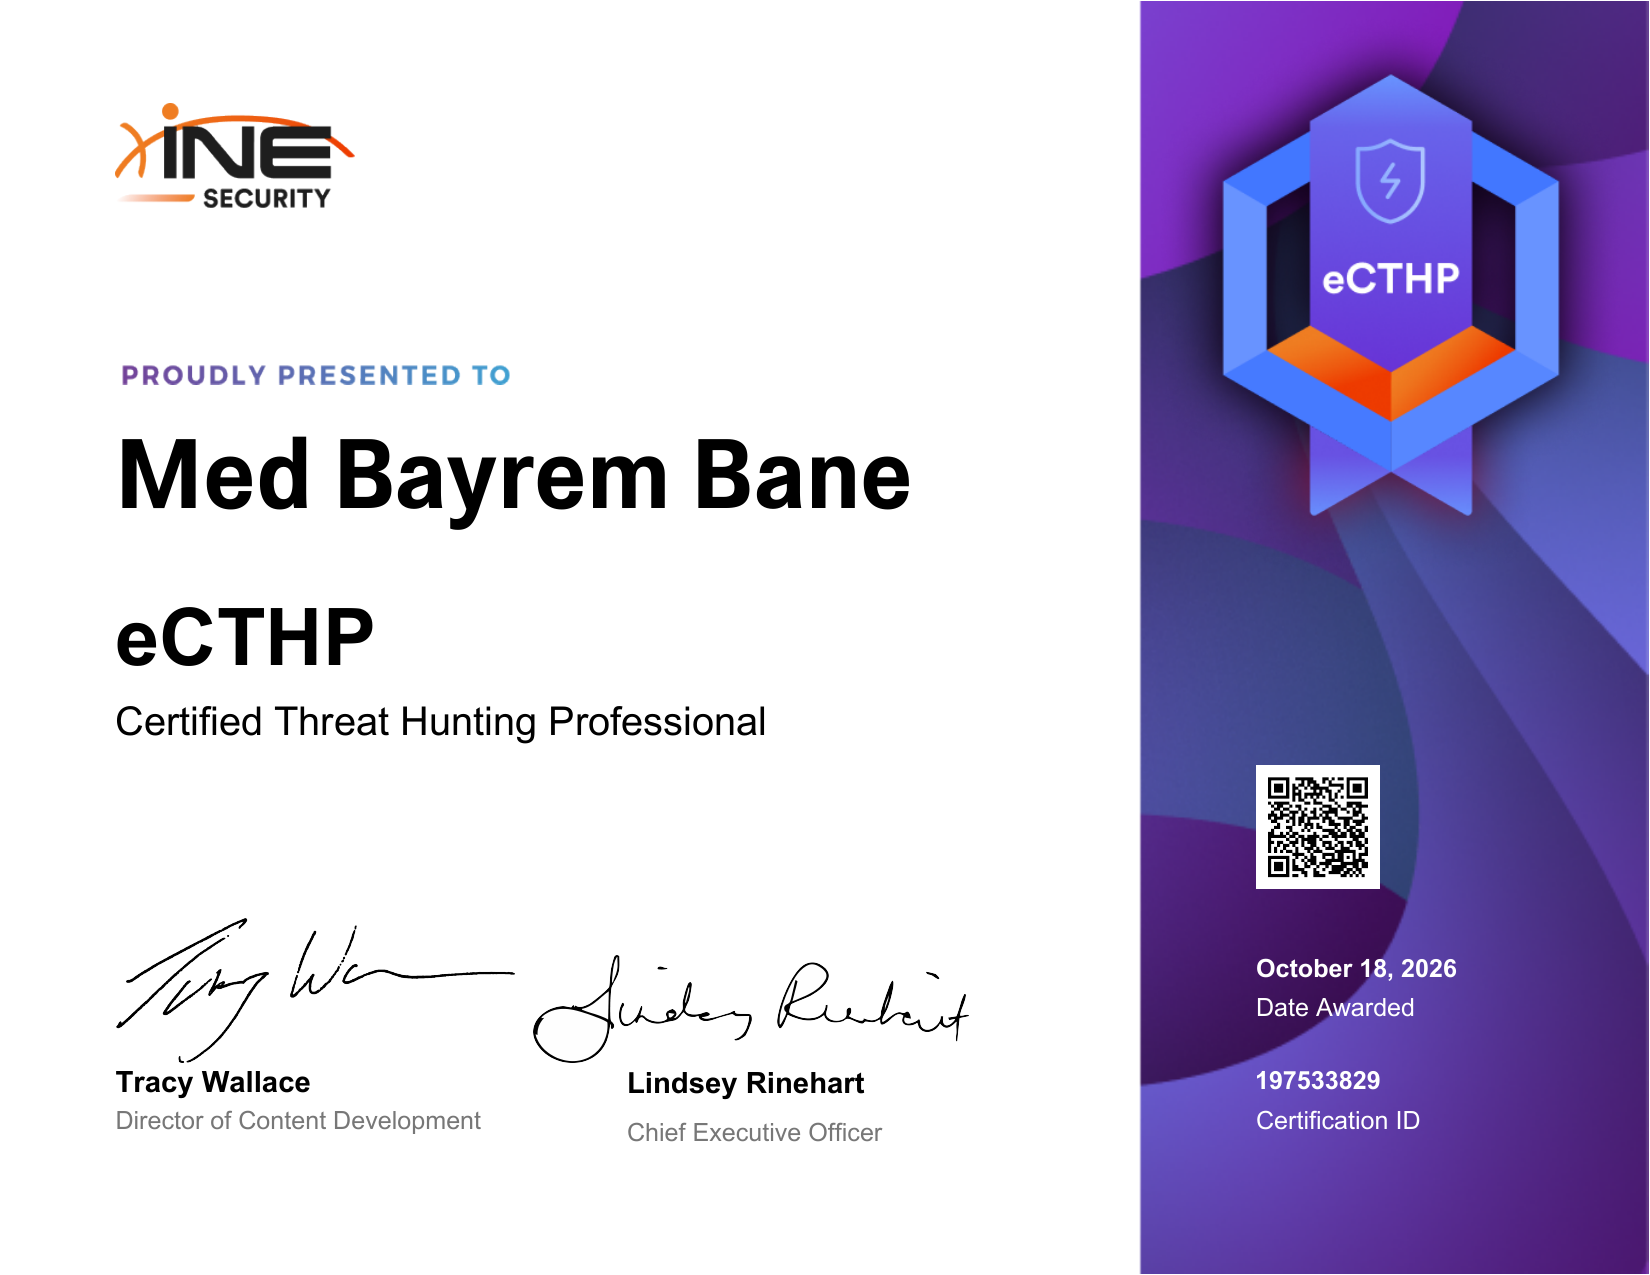
eCTHP is INE’s practical threat-hunting certification: simulated enterprise environments where the job isn’t responding to an alert, it’s finding the compromise before one ever fires.
What I learned
- Threat-hunting methodology: building and testing a hypothesis instead of waiting for a detection rule to catch something.
- Cyber Threat Intelligence as an input: using MITRE ATT&CK and known adversary behavior to decide where to hunt first, not hunting blind.
- Network-based hunting: digging through traffic with Wireshark to spot C2, beaconing and lateral movement that blends into normal noise.
- Endpoint-based hunting: using host telemetry and log data (Splunk/ELK) to surface anomalies in process, auth and file activity.
- Turning a hunch into evidence: documenting a hunt so it either closes clean or hands off a confirmed incident.
Why it matters to my work
This fills the gap between my CTI background and eCIR: CTI tells me what to look for, eCIR is what happens once something’s confirmed, and threat hunting is the proactive middle step — going looking before the SOC’s tools tell me to. It’s the certification that maps most directly onto turning alert fatigue into actually getting ahead of an intrusion.
$ verify --credential
Verify credential →